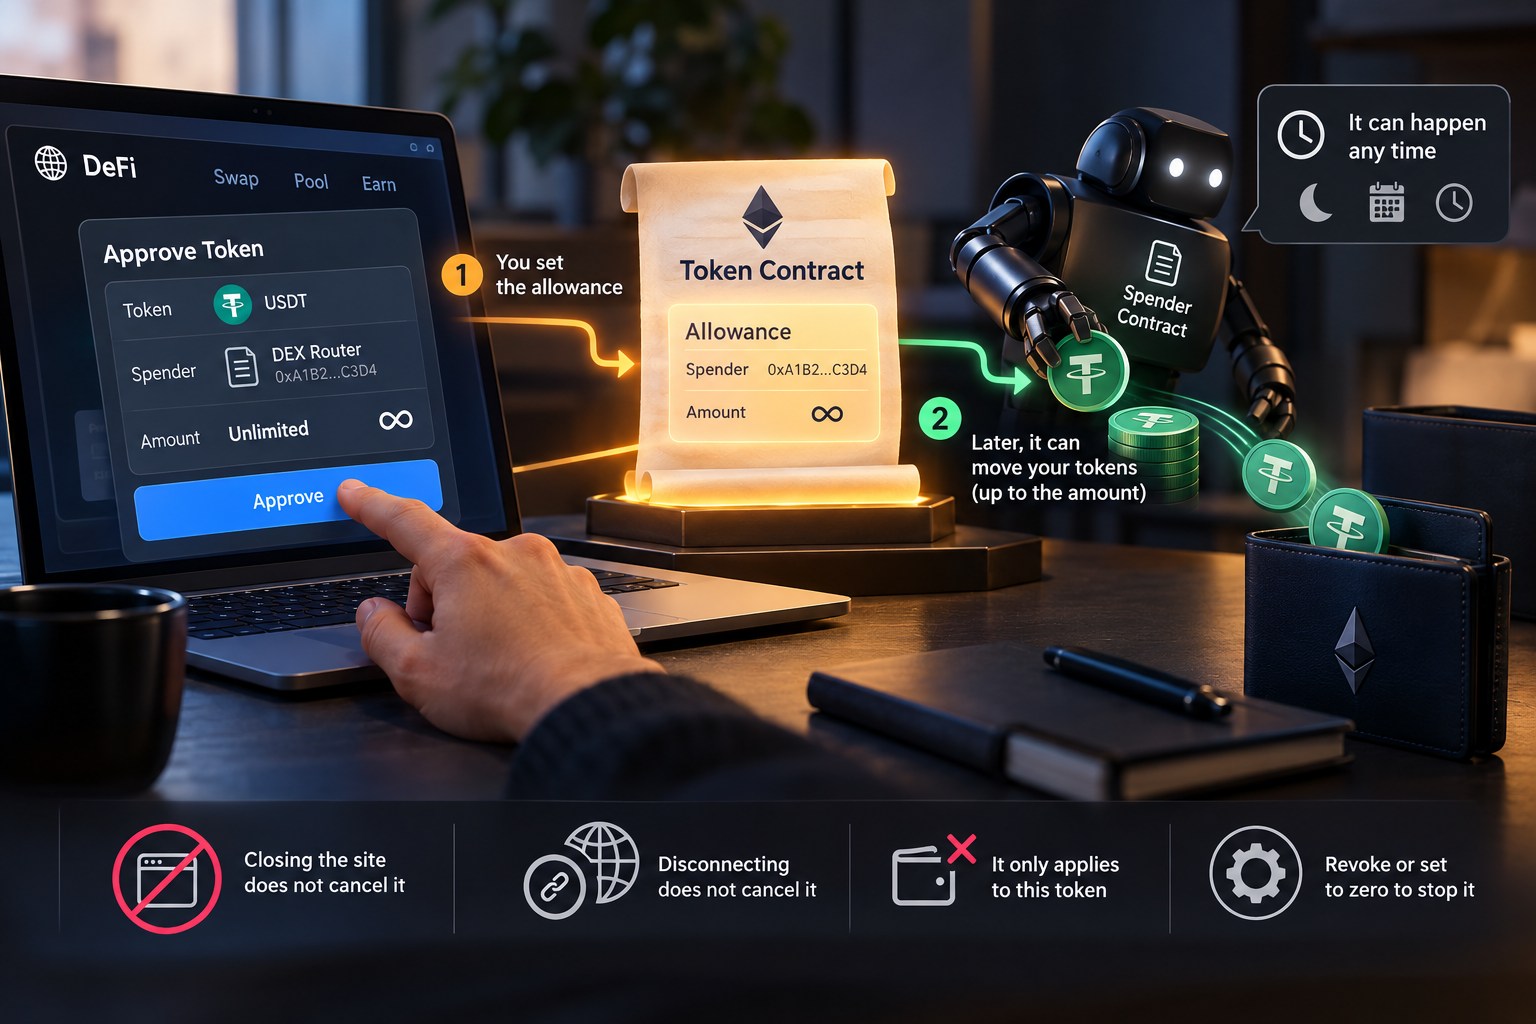
Connecting a website to a wallet lets the site ask for addresses and signatures. An approval is a further step. On an ERC-20 token it records a spender and an amount. Until that record changes, the spender contract can move the token from your address, up to the amount, by sending its own transaction. You do not have to be online when it does.
A budget, not a session
EIP-20 defines the allowance as a stored value. A later call to transferFrom spends it down. There is no session cookie inside the token contract. Closing the browser, disconnecting the site, or switching networks in the wallet interface does not write a new allowance. Only a transaction that sets the allowance, or a spend that reduces it, changes what the spender can take.
The amount is the whole of the permission. If it is the maximum integer the field allows, interfaces say “unlimited.” The contract can then move whatever balance you hold of that token, now or after you receive more, until you set a smaller number. The permission is still limited to that token contract. It does not hand over ETH, and it does not hand over a different token. A second token requires a second approval, which is why a careless session can still be a stack of separate budgets.
What the spender is
The spender is an address, almost always a contract. A decentralized exchange router, a lending pool, and a malicious contract are the same shape at the token layer: an address you named. The token contract does not know which one is reputable. It checks the allowance and the balance. If you cannot explain what the spender will do with the right to call transferFrom, the approval is a blank instruction to a program you have not read.
Some newer tokens add permit-style signatures, specified in designs such as EIP-2612, so a user can sign an approval off chain and let someone else submit it. The stored result is still an allowance. A signature request that mentions a permit, a spender, and a value is the same kind of decision as an approve transaction. It is not “just a login.”
A habit that matches the mechanism
Read the token, the spender, and the amount before you confirm. If the interface offers an exact amount, that amount is the budget you are writing down. Later, read the allowance from the token contract or from a wallet that queries it, rather than from the site that asked. Set an allowance you no longer want back to zero. That is the entire safety content of the mechanism. It does not depend on a particular scam, and it does not require you to guess who an unknown spender “really” is.
What the contract can do after you leave
Once the allowance is stored, the spender does not need your signature again. It needs a transaction of its own, paying its own gas, calling transferFrom with your address as the source. That transaction can arrive minutes later or months later. It can arrive while the site you used is offline. The token contract will not phone home to the website to ask whether you still like the dapp. It will subtract the tokens and the allowance if the numbers work.
The spender’s code decides the destination. A router you intended may forward tokens into a pool as part of a trade you start later. A contract you did not read may forward them to an address that is not a pool at all. From the token’s point of view those are the same call. This is why “I only connected” and “I approved the router” are different losses. The connection revealed an address. The approval armed a contract. Revoking sets the stored number to zero so a later call fails the allowance check. It does not reverse a call that already succeeded, and it does not affect a different token you approved in the same sitting. Read each allowance back from the token contract if you want the number the chain is actually enforcing.
Sources
- EIP-20: Token Standard.
- EIP-2612: permit, an off-chain signature that still results in an allowance.
- Ethereum.org, ERC-20 contract walkthrough.