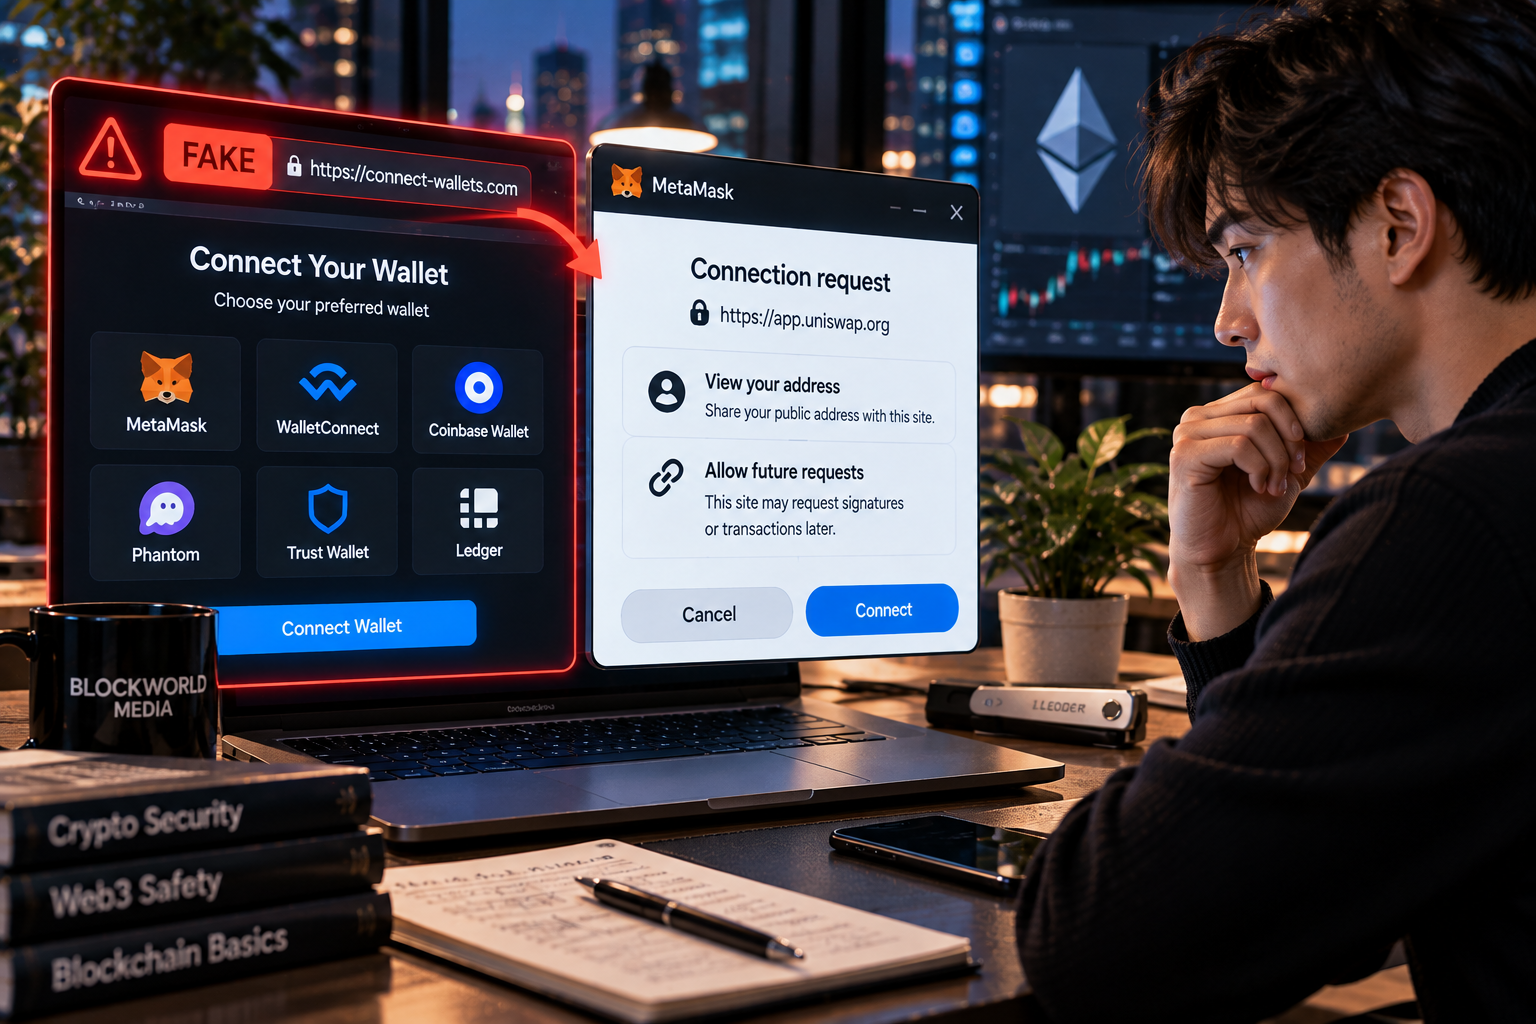
A page can show a wallet logo, a list of browser extensions, and a button that says connect. None of that is produced by your wallet. It is produced by the site, and a copy is as easy as any other web page. The habit that survives that fact is to read the prompt drawn by the wallet software, in its own window, and to know what that prompt is actually asking.
What connect is
In the usual browser-wallet flow, a site asks the wallet to reveal an address and to confirm that this site may send later requests. Ethereum’s documentation of connecting to a dapp describes that step as an introduction, not as a transfer. A plain connection does not move ETH and does not set a token allowance. It does tell the site which address you are using, and it opens a channel for the next request. That next request can be a signature, a permit, or a transaction. Each of those is a separate confirmation.
A copied front end will try to blur the sequence. The fake page looks like the wallet. The real wallet, if it opens at all, is another window, usually with the extension’s own chrome and a URL or an origin you can inspect. A page that asks you to type a seed phrase, a private key, or a hardware-wallet PIN into the browser is not a connection prompt. Wallet software does not need the phrase in order to connect. The phrase is the key material itself.
Read the request, not the website’s caption
Wallet prompts are specific. A signature of a human-readable login string is not an approval, though you should still read what is being signed, because signatures can be structured data. A transaction prompt shows a destination, a value, and data. A permit or an approve names a token, a spender, and an amount. The site’s caption above the button, “verify your wallet” or “claim,” is not one of those fields. If the caption and the wallet prompt disagree, follow the prompt, and cancel it if the fields are not what you came to do.
Also read the origin. A bookmark or a typed address is a weaker story than a link from a search ad or a reply on social media. This does not require you to decide, from the outside, which brands have been copied this month. It requires you to notice that the picture of a connect button is not the wallet, and that the wallet will ask separately before it spends, signs, or approves. If there is no wallet prompt at all, nothing from your keys has been authorized, whatever the page claims happened next.
The wallet’s request has a type
EIP-1193 is the interface a site uses to talk to an injected wallet. The methods are not interchangeable, even though a copied page can label all of them “connect.” A request for accounts asks the wallet to share an address. A request to sign a message asks for a signature and does not, by itself, broadcast a transaction. A request to send a transaction asks the wallet to authorize a state change, with a destination, a value, and data. A careful wallet shows those fields in its own window. The page underneath can show a cropped picture of some other wallet’s window. The picture cannot sign. Only the real prompt can, which is why the fields inside the real prompt are the ones to read, and why a prompt that asks you to type the seed into a text box is not one of these methods at all.
After you cancel, the page may still say the connection succeeded. That sentence is content on the page, like any other sentence. Refresh nothing, sign nothing, and check the wallet’s own list of connected sites if it has one. Disconnecting there, or ignoring the site, does not require you to interact with the copy again. The copy’s only tool is the next prompt it can persuade the real wallet to open.
Sources
- Ethereum.org, introduction to dapps, including the distinction between a connection and later transactions.
- EIP-1193, Ethereum Provider JavaScript API, the interface a site uses to request accounts and send requests to a wallet.
- EIP-712, typed structured data hashing and signing.