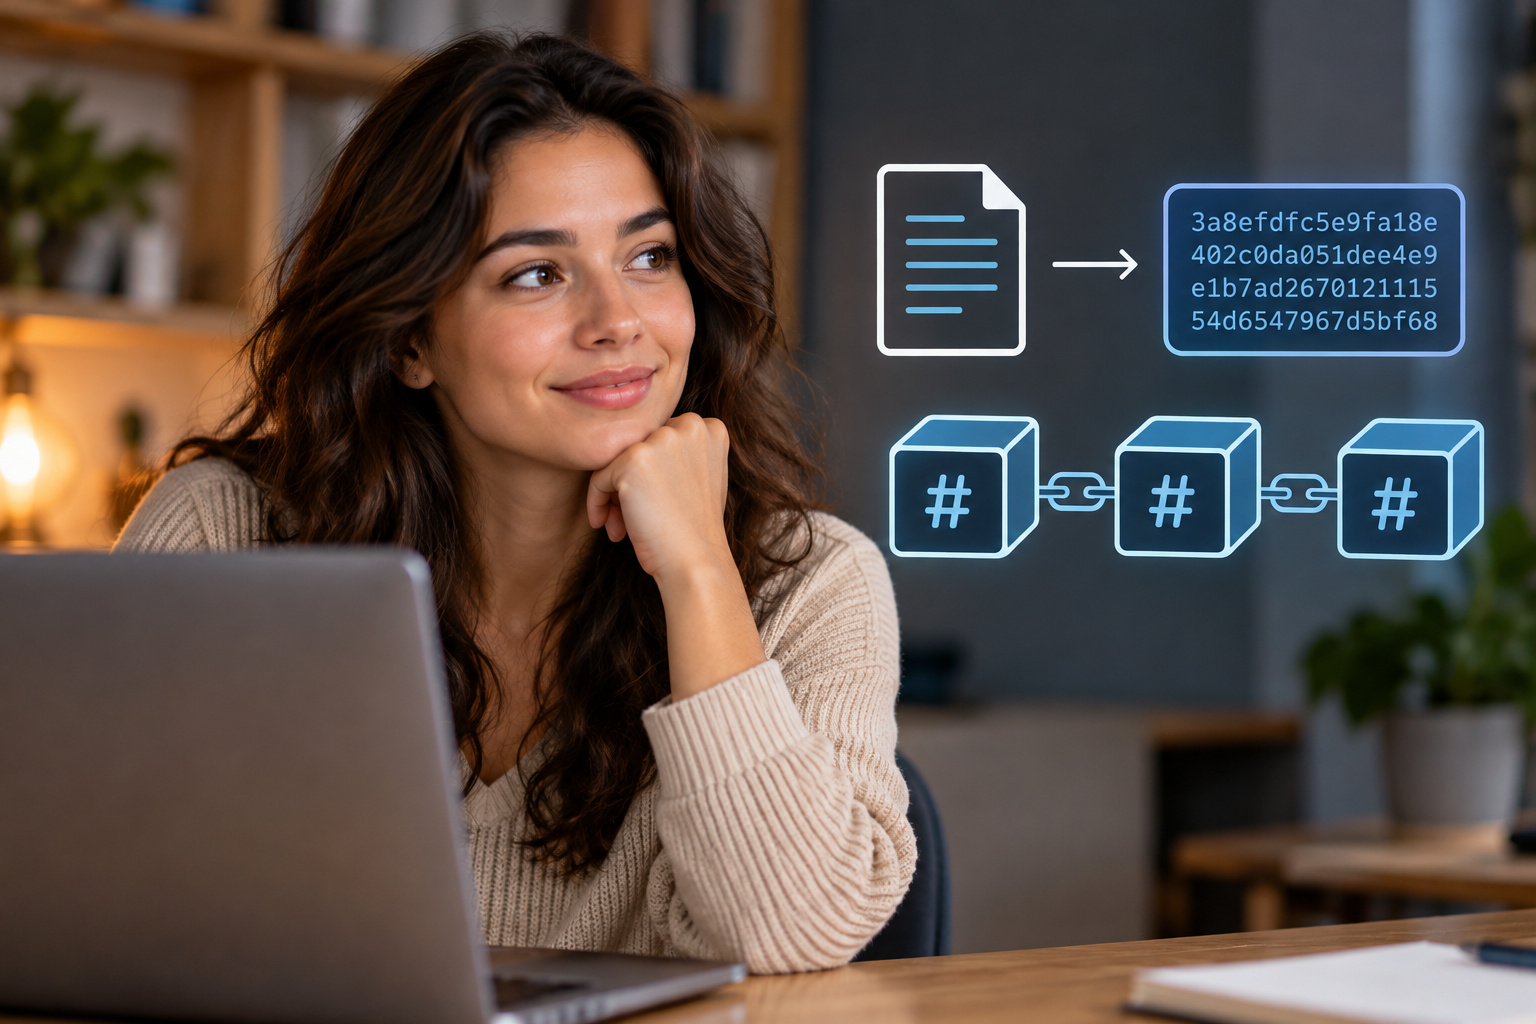
A cryptographic hash function takes an input and returns a fixed-size digest. Feed it a sentence, a block header, or an empty file, and you get a short string of bytes. Change one bit of the input and the digest changes in a way you cannot usefully predict. Blockchains lean on that behavior whenever they need a short name for a long piece of data.
The properties the chain actually uses
NIST’s Secure Hash Standard, FIPS 180-4, specifies SHA-256 and the other SHA-2 functions. Bitcoin uses SHA-256, twice, on the block header. The properties that matter here are not the internal rounds. They are the promises users rely on. It is infeasible to start from a digest and recover an unknown input. That is preimage resistance. It is infeasible to find two different inputs with the same digest. That is collision resistance. And the same input always produces the same digest, which is why a node can recompute a hash and compare.
Those promises are what let a block header name its parent. The parent is summarized by a hash. They are what let a Merkle root name a list of transactions. They are what a proof-of-work miner is searching over: not a secret, but a header whose hash lands below a target. Checking the work is cheap because hashing one header is cheap. Finding the header was expensive because the target is low.
What a hash does not do
A hash does not hide data. If the input is a known set of possibilities, someone can hash them all and see which digest matches. Hashing a password slows that search only when the password is hard to guess and the hash is built for passwords. SHA-256 by itself is not a password-storage scheme, and it is not encryption. Encryption is reversible with a key. A hash is not meant to be reversed.
A hash is also not a signature. A signature proves that a particular private key was used on a particular message. A hash proves nothing about who produced the input. Anyone can hash anything. In a transaction, the hash identifies data. The signature, or the script, is what authorizes spending. When a write-up says a block is “encrypted by miners,” it has swapped these tools. The block is public. The hash is a name and, in proof of work, a puzzle.
The practical test is small. If you can recompute the digest from the data, you do not need to trust someone else’s label for that data. If you cannot get the data, the digest is only a label. It does not carry the underlying block, and it does not tell you the block was valid. It tells you which bytes were hashed.
A digest you can recompute
SHA-256 of the nine characters blockworld, in UTF-8 and with no newline, is 3a8efdfc5e9fa18e402c0da051dee4e9e1b7ad267012111554d6547967d5bf68. Change the word by a single character and the digest is unrelated. You do not need a blockchain to see the property. You need any implementation of the function NIST specified. Bitcoin then applies that function twice to a block header, and requires the result to fall under a target. The second hashing is a protocol choice, not a different kind of magic. The header is still public. The digest is still a name for those bytes.
The same function is how a Merkle tree compresses a list, and how an address commits to a key or a script. In each case the chain stores the digest, or a digest of a digest, because the digest is short and because changing the underlying bytes would be caught. None of those uses encrypts the underlying bytes. A transaction that has been hashed is still a transaction anyone who has it can read. The hash lets other people refer to it without repeating it. If a write-up says the chain “encrypts” transactions so that miners can unlock them, it has mixed up a digest, which anyone can recompute, with a ciphertext, which only a key holder can reverse. A digest names bytes. A ciphertext would hide them.
Sources
- NIST FIPS 180-4, Secure Hash Standard.
- Bitcoin white paper, on hashing for proof of work and Merkle trees.
- NIST glossary, preimage resistance.