“Inherits the security of Ethereum” has become a product sentence. It is worth pinning to a mechanism. A system inherits a base layer’s security when a user can rely on the base layer, and not on a particular operator’s honesty, to get a stated result. Usually that result is: a valid withdrawal cannot be blocked forever, and an invalid withdrawal cannot be finalized. If the mechanism does not provide that, the sentence is advertising.
What has to be true
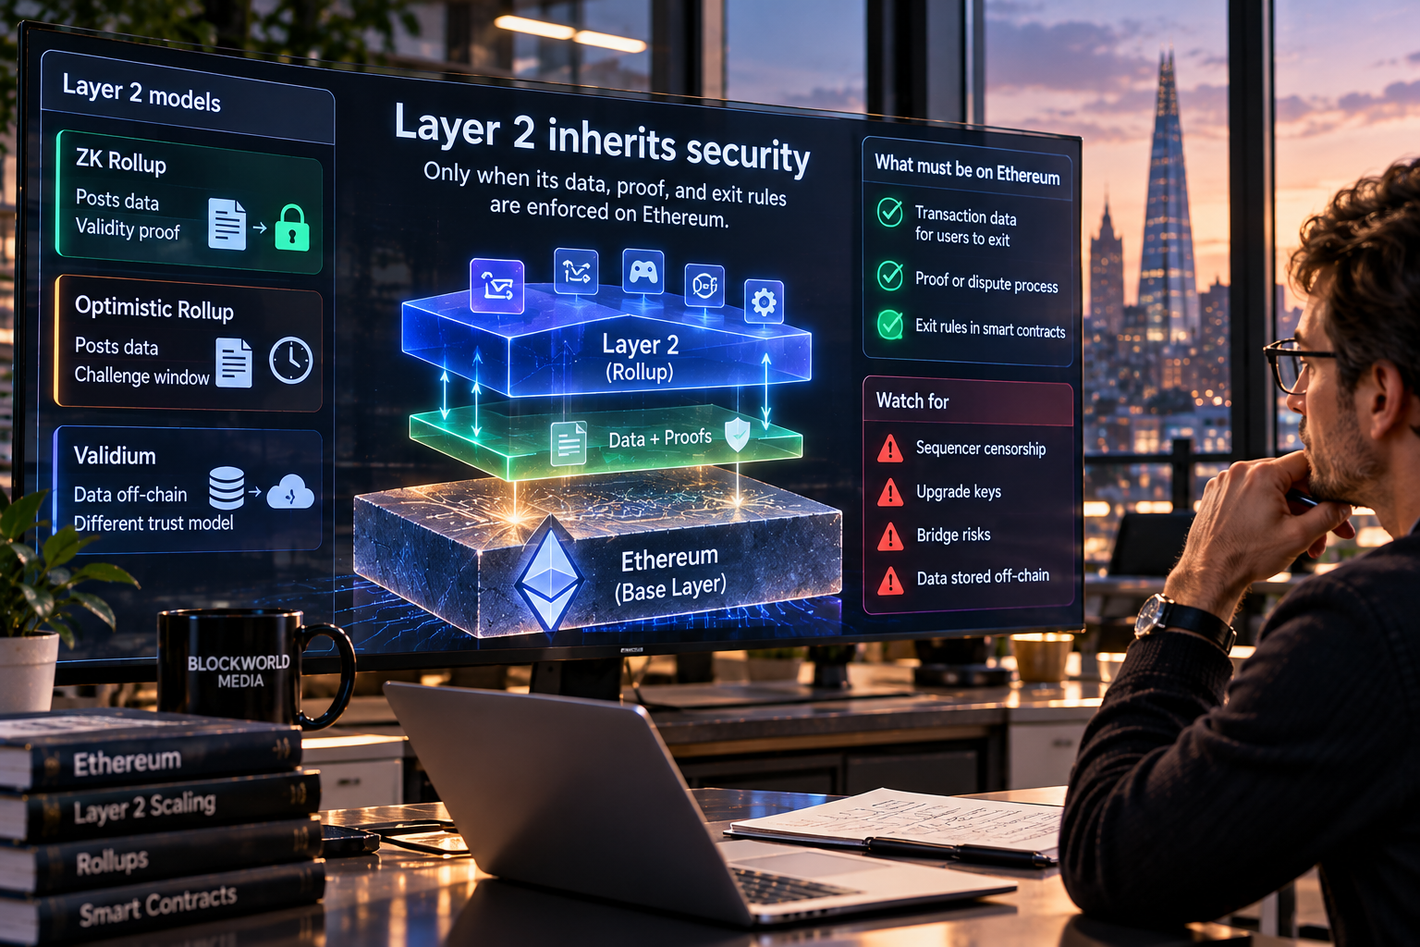
Ethereum.org’s layer-2 pages describe rollups as systems that post enough information to the base chain for the base chain to check their work, either with a validity proof or with a dispute process. In a validity-proof design, often called a zk-rollup, a proof that the state transition was correct is verified by a contract on the base chain. In an optimistic design, the state is proposed and can be challenged during a window. Both designs are trying to make the base contract the referee.
The referee can only judge what it can see. If the data a user needs in order to reconstruct the state, or to build a proof, is posted on the base chain, users can exit even when the operator disappears. If that data lives only with a committee, the base chain cannot reconstruct the state. Ethereum.org discusses this under data availability. A system that stores data elsewhere, sometimes called a validium, can still be useful. It does not inherit the same exit guarantee. Calling both of them “an Ethereum layer 2” without the distinction erases the guarantee people thought they were buying.
Operators, upgrades, and bridges
A sequencer that orders transactions can censor in the short run. Inheritance, if the design has it, means there is another path: force a transaction through the base contract, or withdraw from data that is already posted. If that path does not exist, censorship by the sequencer is not a temporary inconvenience. It is the security model.
Upgrade keys matter just as much. A contract controlled by a multisig that can swap the proof verifier, change the bridge, or seize funds is a different system from a contract nobody can change. Many production rollups have used upgrade keys, sometimes with a delay. That is a published operational choice. It means there is a set of key holders who can alter the rules a user thought the base chain had frozen. “Inherits Ethereum security” is then true only inside the limits of that key. The honest sentence names the delay and who can act before it expires.
A bridge token is a narrower claim again. A token on one chain that is “backed” by an asset locked on another chain depends on the bridge’s signers or its proof system. A failure of the bridge does not become a failure of the base chain’s consensus, and a secure base chain does not repair a bridge that will sign an unauthorized release. The asset you hold is a claim on the bridge’s rules.
A sentence that can be checked
Ask where the data is posted, who can prove a bad state wrong, how long that takes, and who can upgrade the contracts. If those four answers live on the base chain, the inheritance claim has content. If any of them live with a company, the system may still be a reasonable place to transact. It inherits that company’s operations, plus whatever piece it really did pin to the base layer. The precise sentence is the useful one.
Time is part of the sentence. Ethereum.org describes optimistic rollups as posting data and waiting, typically on the order of seven days, so that someone can challenge a bad state. That figure is a design choice those rollups publish, not a law of every layer 2. A validity proof does not need the same wait, because the contract checks the proof before accepting the state. It still needs the data if users are to reconstruct their own balances and exit. A seven-day window you cannot use, because the data was never posted, is not a window. A proof you cannot verify, because an upgrade key replaced the verifier, is not a proof. The slogan survives only where those mechanisms are the ones a contract will actually run.