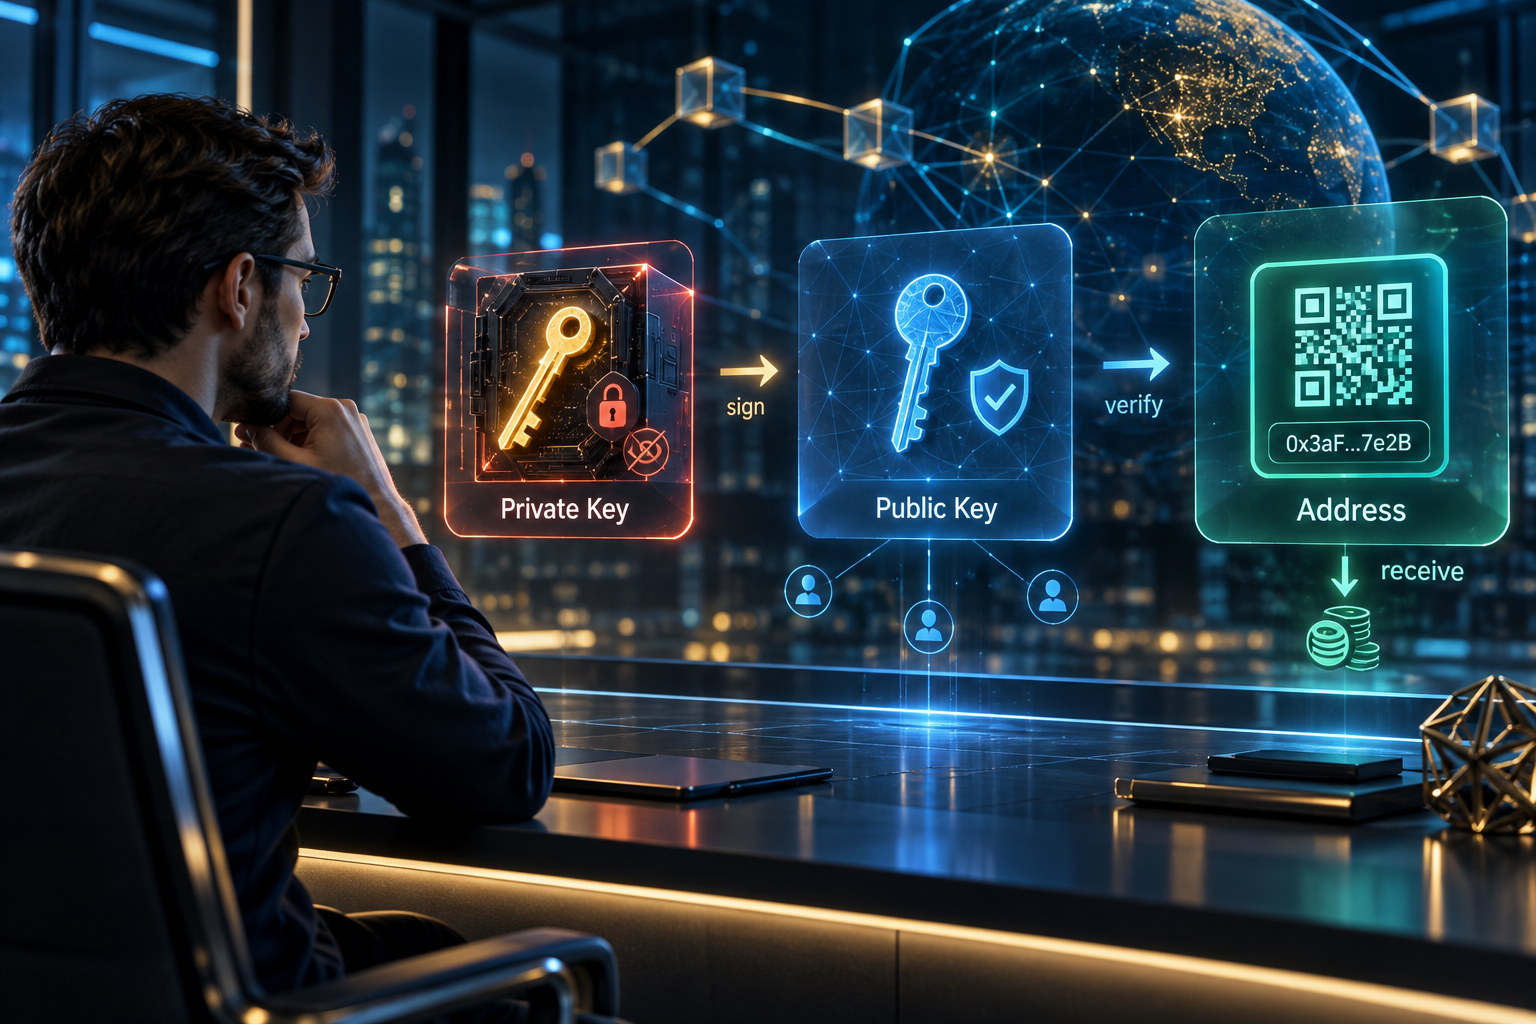
Wallet screens compress three different objects into one QR code. The private key is the secret that can authorize a spend. The public key is derived from it and can be shared when a signature has to be checked. The address is what you usually hand to a payer, and it is not the same bytes as either key. Treating the address as “the public key” is close enough to cause a real misunderstanding.
The featured image labels the arrow from the private key to the public key as sign, and the arrow onward to the address as verify. Those labels describe the wrong steps. A public key is calculated from the private key. An address is then derived from the public key, or from a script, depending on the address type. Signing is separate: the private key authorizes one transaction, and the public key is what lets someone else check that signature.
What each object is for
On Bitcoin and Ethereum, the keys used in ordinary wallets are elliptic-curve keys. The private key is a large random number. The public key is a point on the curve computed from that number. The computation is easy in one direction. The reverse, recovering the private key from the public key, is the problem the scheme assumes no one can solve. NIST’s digital-signature standard describes the signature algorithms. FIPS 186-5 specifies ECDSA, and the curves it recommends for federal use do not include secp256k1. Bitcoin uses ECDSA on that curve, with its own encoding. Ethereum accounts use the same curve, with a different way of turning a signature into an address check.
A signature is produced with the private key over a specific message, usually a hash of the transaction. Anyone with the public key can check it. A signature is not the private key, and broadcasting it does not, by itself, reveal the private key. Losing the private key is a different failure: nothing in the chain stores a copy for you.
Why an address exists
An address is a commitment to a spending condition, shortened and equipped with a checksum so a typo is more likely to be caught. In current Bitcoin practice, a common address commits to a script that will require a public key and a signature when the coins are spent. The public key itself need not appear until that moment. On Ethereum, an externally owned address is the trailing bytes of a hash of the public key. The account model then stores a balance at that address. In both designs, the address is safer to display than the private key, and it is still not something you can “log in” with. Paying to an address gives the funds to whoever can satisfy the condition later.
A seed phrase, specified for many wallets by BIP 39, is a backup of the secret material from which private keys are derived. It is not an address, and it is not a public label. Anyone who has the phrase can derive the keys. Publishing an address is the ordinary way to receive a payment. Publishing a seed phrase is the ordinary way to lose one.
When you check a wallet, separate the three. The address is what a payer needs. The public key is what a verifier may need once a signature exists. The private key, or the seed that creates it, never needs to leave the signing device in order for a payment to be checked.
Addresses are commitments, and there are several kinds
Bitcoin has used more than one commitment format. A legacy pay-to-public-key-hash address commits to a hash of a public key. A pay-to-script-hash address commits to a hash of a script. Native SegWit, specified in BIP 173, puts a witness program in a bech32 address. Taproot, specified in BIP 341, commits to a tweaked key, which may also hide a tree of scripts. Those Taproot addresses use bech32m, the checksum format specified in BIP 350. A payer does not need to reconstruct any of that. A payer needs to copy the address the receiver generated. A recovery tool does need to know which formats the original wallet used, because a key derived from the seed will not find coins locked to a script the tool never generates.
Ethereum’s common account address is shorter and looks simpler: 20 bytes, shown as hexadecimal, derived from the public key. Contract addresses are the same length and are not derived from a key the user holds. They are derived from the creator. A transaction to a contract account is a message call, and the account code runs when that call arrives. A transfer with empty calldata can still run receive or fallback code. It does not simply increase a balance while leaving the code untouched. The characters on the screen do not say which of those you are doing. The wallet’s transaction preview does, if you read the destination and the data field rather than the address alone.
Sources
- NIST FIPS 186-5, Digital Signature Standard.
- Bitcoin Developer Guide: wallets.
- BIP 39, mnemonics.
- Ethereum.org, accounts, on how an externally owned address relates to a key.
- BIP 173, on bech32.
- BIP 341, on Taproot commitments.
- BIP 350, Bech32m format for v1+ witness addresses.