A block can hold thousands of transactions. A light client does not want all of them. It wants one. A Merkle tree is the construction that lets the client check that one transaction was included in a block header, by downloading a short path of hashes instead of the block body. Inclusion is the word to keep. The proof does not do the rest of a full node’s job.
The tree in the white paper
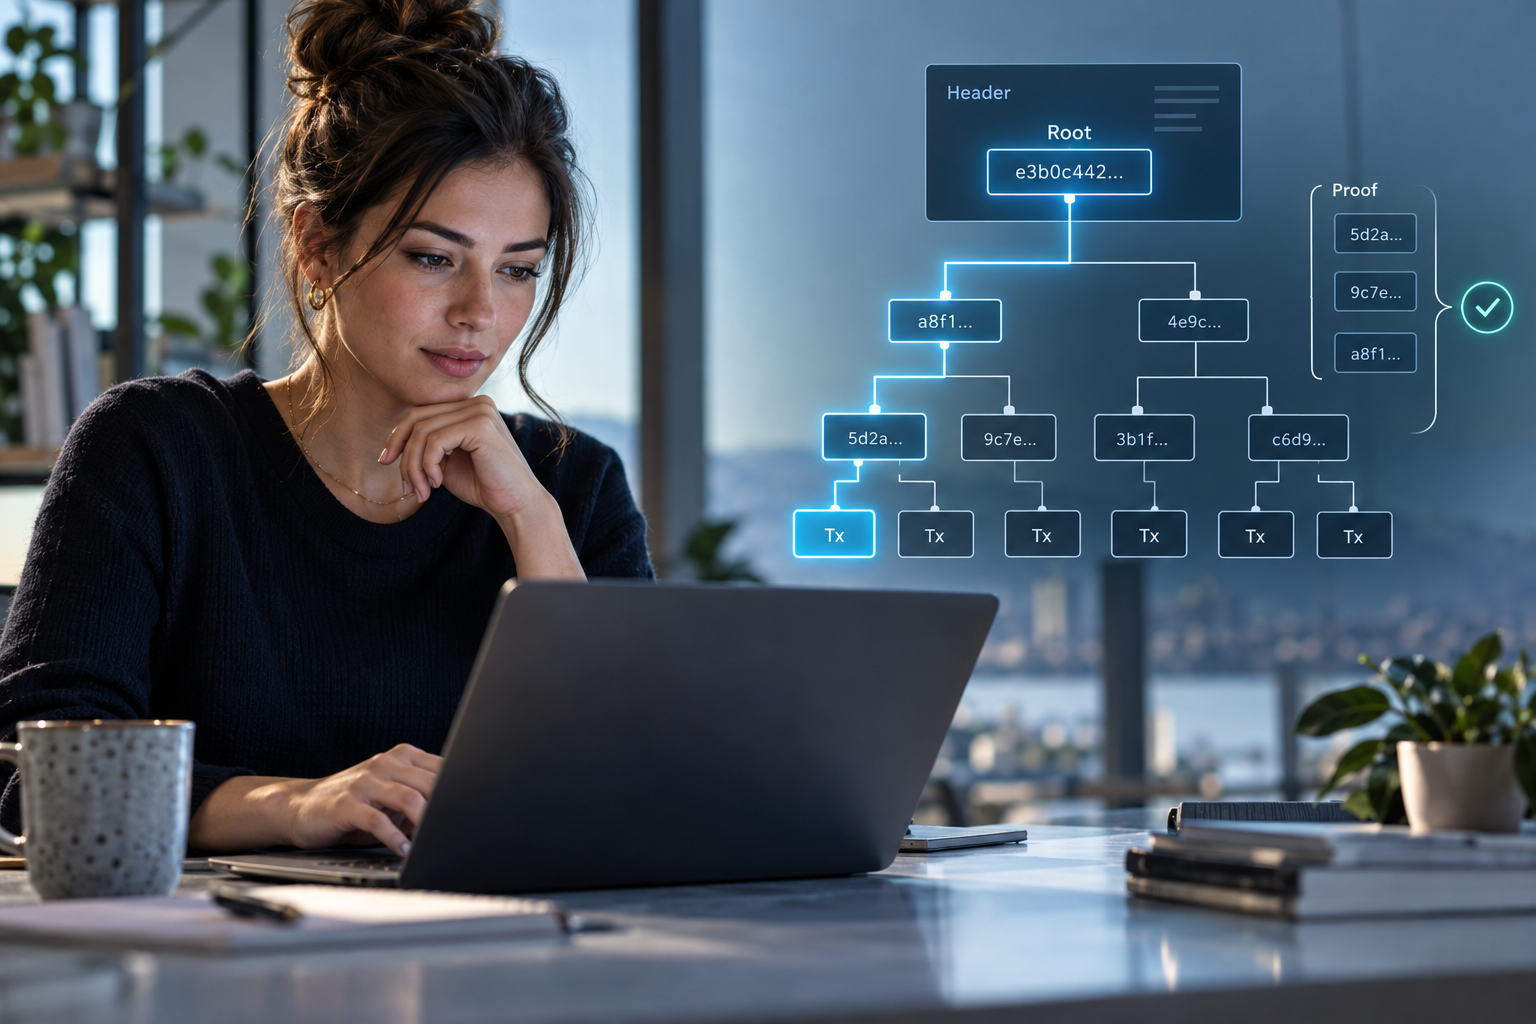
The Bitcoin white paper’s diagram is still the clearest version. Transactions are the leaves. Adjacent hashes are concatenated and hashed again, and that process repeats until one hash remains. That hash is the Merkle root. It goes in the block header. Change any transaction, or swap two of them, and every hash above the change is different, including the root. A node that has the header therefore has a commitment to one specific ordered list.
Bitcoin hashes the leaves and the internal nodes with double SHA-256. If the list is an odd length at any level, the last hash is paired with itself. Those are implementation details a programmer has to get right. The idea does not depend on them: the root is a fingerprint of the whole list, and a path from one leaf to the root is a fingerprint of that leaf’s place in the list.
What the light client is given
Suppose a client cares about transaction T. A full node can send T, plus the sibling hash at each level from T up to the root. The client hashes T, combines it with the first sibling, hashes that, combines the result with the next sibling, and continues until it has a root. It compares that root with the Merkle root in the header it already stores. If they match, T is in the list that header commits to. The siblings are the proof. They are small because each level contributes one hash, and the tree is balanced. A list of a thousand transactions does not require a thousand hashes in the proof.
The white paper calls the broader technique simplified payment verification. The client also looks at the chain of headers and at how much proof of work sits on top of the block. The Merkle path answers “is this transaction in this header?” The header chain answers “how much work followed this header?” Together they are still not the question “would a full node accept this transaction under every consensus rule?”
The holes in an inclusion proof
A transaction can be included and still be invalid if the miner who built the block broke a rule and the client is not checking. A light client that only checks inclusion will not notice a forged script, an inflated subsidy, or an output spent twice, unless those failures happen to be visible in the headers. The white paper says this directly: the method works while honest nodes control the network and becomes vulnerable if an attacker overpowers it.
The proof also says nothing about transactions that are absent. Failing to find a proof is not, by itself, a proof of absence, unless the client has the full list or a structure built for that question. And a Merkle proof reveals the transaction and its path to whoever assembles it. Privacy is a separate design. Compact block filters, specified later in BIP 157 and BIP 158, are one way for a client to learn which blocks might contain its payments without asking a server for a particular transaction. They complement inclusion proofs. They do not replace validation.
The same shape, elsewhere
Ethereum uses Merkle-Patricia trees for state, transactions, and receipts. The hashing details and the way keys are arranged differ from Bitcoin’s binary transaction tree. The client-facing claim is the same shape. A root in a header commits to a large structure, and a path of hashes lets someone check one entry. A proof of an account balance in a state root shows that this root commits to that balance. It does not show that you agree with the chain that produced the root.
When you are handed a proof, ask three questions. Which root is it checked against, and do you have that header from somewhere you accept? What exactly is the leaf: a transaction, an account, a receipt? What does a match fail to prove: validity of every rule, absence of other transactions, or the honesty of the server that handed you the siblings? If the answers are clear, the tree is doing the job it was built for.
A tree small enough to recompute
The arithmetic is ordinary SHA-256, which is why a toy tree is worth doing by hand. This toy uses one SHA-256, so the bytes are easy to check. Bitcoin’s transaction tree uses two. The shape is the same.
Take two leaves whose contents are the single characters a and b. SHA-256 of the character a is ca978112ca1bbdcafac231b39a23dc4da786eff8147c4e72b9807785afee48bb. SHA-256 of the character b is 3e23e8160039594a33894f6564e1b1348bbd7a0088d42c4acb73eeaed59c009d. Hash the raw 32-byte digest of a concatenated with the raw 32-byte digest of b, and the parent is e5a01fee14e0ed5c48714f22180f25ad8365b53f9779f79dc4a3d7e93963f94a. Anyone can recompute those three hashes. If a server claims the root is that parent, and sends you the leaf a plus the sibling digest of b, you can rebuild the parent. If it sends you a different sibling, you will not.
Scale that up and the client still never needs the leaves it does not care about. It needs its leaf and one sibling per level. A dishonest server that wants to put a different transaction under the same root has to find bytes that hash to the same parent. Collision resistance is the assumption that this will not happen. The assumption is about the hash, not about the server’s honesty. The server can still hand you a proof for a different root, which is why the client must already have the header from a source it accepts. A proof that checks against a header the attacker invented is a proof about the attacker’s header.
Inclusion, validity, and absence
Write the three outcomes in separate sentences and the tree stops being mystical. A matching path means this leaf is in the list committed by this root. It does not mean every consensus rule was applied to the leaf. It does not mean some other leaf is absent. Absence needs the full list, or a different structure built to prove gaps. Bitcoin’s header commits to one transaction root. A light client that stops at a matching path has finished the inclusion question and left the validity question to full nodes and to the work on the header chain.
Ethereum’s Patricia trie makes the same split with more machinery. Keys are paths through a tree that also commits to account state, so a proof can show a balance, a nonce, or a piece of contract storage under a state root. The extra machinery does not remove the need to trust, or to check, the header that holds the root. A proof is a path. A header is a claim that this path is the one the chain accepted. A full node is the software that decides whether the chain was entitled to accept it.
Sources
- Bitcoin white paper, Merkle trees and simplified payment verification.
- Bitcoin Developer Reference: block chain, on the Merkle root in the header.
- BIP 157 and BIP 158.
- Ethereum.org, Patricia Merkle Trie.