People talk about a smart contract as if the chain stored a readable program: the Solidity file, the comments, the function names. What an Ethereum client stores for a contract account is code in the Ethereum virtual machine’s bytecode, plus storage. The source text is a developer artifact. It matters, but it is not what the protocol runs.
From a source file to an address
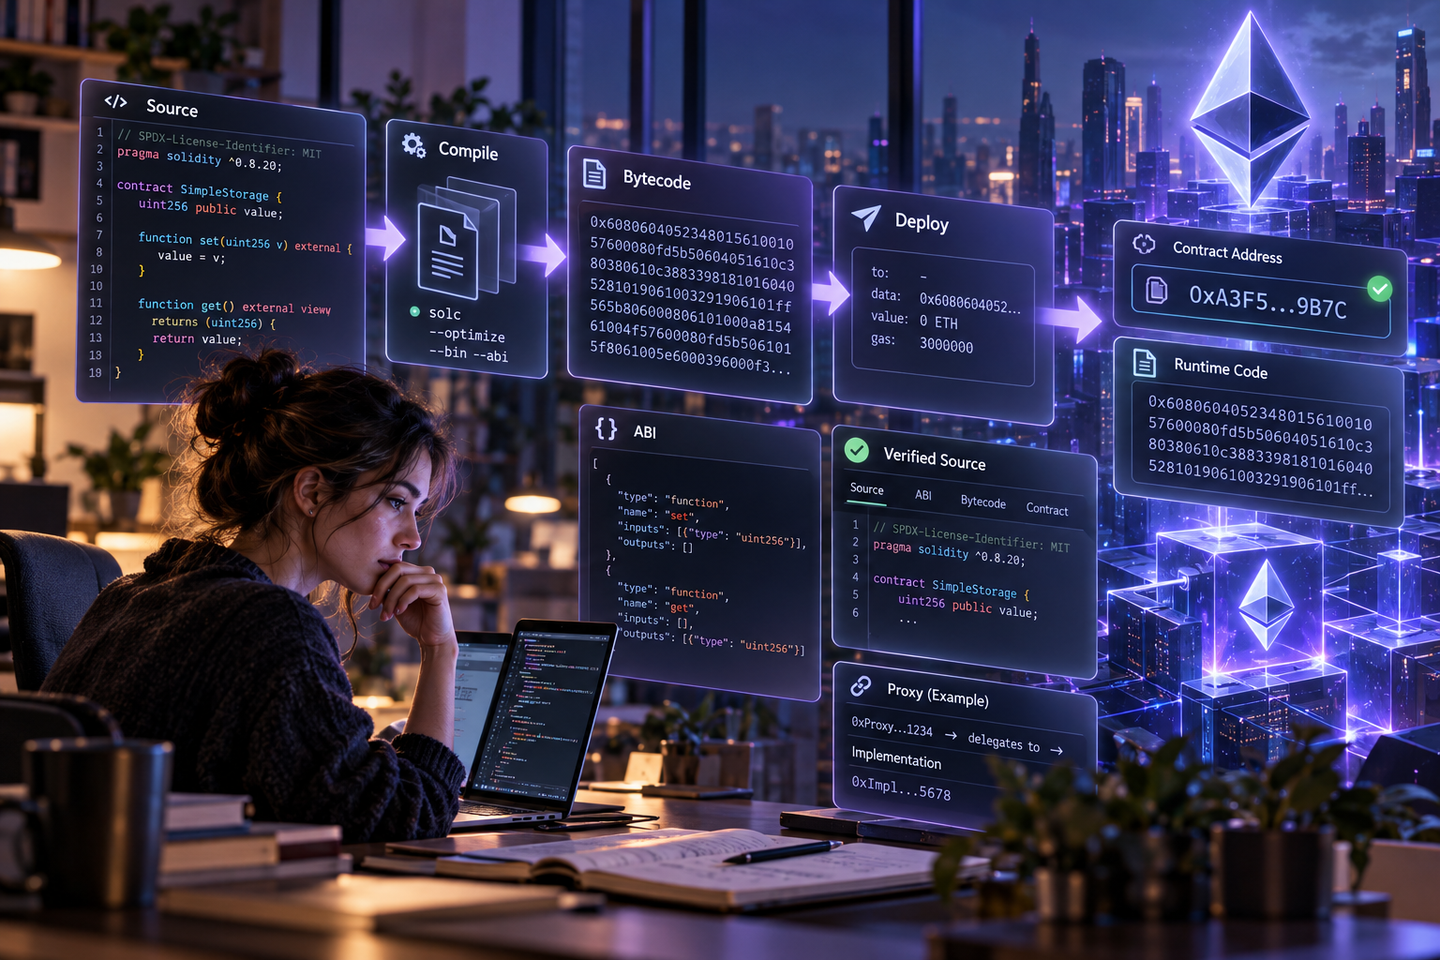
A developer writes source, usually in Solidity or Vyper, and compiles it. The compiler produces bytecode and an application binary interface, the ABI, which describes how to encode calls. A creation transaction sends the init code. The virtual machine runs that init code once. The code it returns is what gets saved as the contract’s code. The address is determined by the creator and the creator’s nonce, unless a different creation path such as EIP-1014 is used.
After that, a call to the address executes the stored bytecode in the context of that account’s storage. Function names survive only if someone kept the ABI or the source. The chain sees selectors, the first four bytes of the hash of a signature, and encoded arguments. If the bytecode has no path for a selector, the call does not do what the function name in an old blog post suggested.
What “verified” means on an explorer
Block explorers let a publisher upload source and compiler settings. The explorer compiles that source and checks whether the bytecode matches what is on chain. A match is evidence that this source could have produced this code under those settings. It is not the chain storing the source. It is not a promise that the publisher is the only person who understands the code, or that the code does something desirable.
A failed verification means you do not have that particular check. It does not mean the contract is empty. The bytecode is still there. Someone can still call it. Reading bytecode is slower than reading Solidity, which is why the source match is useful, and also why a badge is not a substitute for knowing which address you are calling.
The questions bytecode can and cannot answer
Bytecode can show which operations are possible: who can move a balance mapping, whether a function can change an admin, whether the contract can call another address with arbitrary data, whether it can self-destruct or upgrade by pointing at a new implementation. Those are properties of the code that will run.
Bytecode cannot show the author’s intent beyond what the code does. Comments are not on chain. A function named rescue in a verified source is only as comforting as the body of that function. An upgradeable contract adds another layer: the address you call may hold a proxy, and the code that matters may be the implementation address stored in a slot. Matching source on the proxy alone does not describe the implementation.
A practical reading order is short. Identify the address. Decide whether you are looking at a proxy. Obtain bytecode, and source only if it reproduces that bytecode. Then read the functions that can move assets or change who is allowed to move them. The chain will not consult the README.
Compilers are part of the evidence
The same source can produce different bytecode under different compiler versions and optimizer settings. That is why a serious verification records those settings. It is also why “we published the code on GitHub” is a weaker statement than “this commit, compiled with this configuration, matches this address.” The GitHub file can change. The bytecode at the address does not change unless the contract’s own rules replace it, which itself is something the bytecode has to allow.
None of this makes source irrelevant. Audits, tests, and readable code are how humans notice mistakes before deployment. After deployment, the deployed code is the authority. If the source and the bytecode disagree, follow the bytecode.
Init code is not the code that stays
A creation transaction carries init code. The virtual machine runs it once. The bytes that init code returns are the runtime code stored on the account. Constructors, deployment-time checks, and the setting of the first owner live in the init code. They do not remain as callable functions unless the returned bytecode includes them. Reading a verified source, you are usually looking at both phases at once. Reading an explorer’s “deployed bytecode,” you are looking only at what was returned. A check that existed solely in the constructor cannot be called later, and it also cannot be undone later.
Compilers append extra bytes that are not executable. Solidity can attach a metadata hash, a fingerprint of the source and the compiler settings, after the runtime code. A swarm or IPFS-style hash at the end of a bytecode blob is a pointer to that metadata. It is not a function. It does not put the source on chain. It is useful because two deployments with the same metadata hash were probably built from the same inputs, and a mismatch is a reason to look harder. It is not, by itself, verification. Verification is still “compile this source with these settings and compare.”
Delegation is still bytecode
Many contracts people call upgradeable are proxies. The address you hold in a wallet stores a short piece of bytecode whose job is to forward calls to an implementation address kept in storage. Under a delegate call, the implementation’s code runs, but the storage it writes is the proxy’s storage. The implementation address can hold the logic. The assets sit in the proxy. Matching source code on the implementation does not tell you who is allowed to change the implementation slot. That rule is in the proxy’s bytecode, or in a separate admin contract. “The code is verified” is incomplete until you say which address.
There is a narrower pattern worth naming because it looks like an empty account. EIP-7702, and earlier experiments with delegated accounts, let an externally owned account point at code. The account can then behave like a contract for some calls. The precise rules depend on the upgrade you are reading. The reading habit does not. Ask which code will actually run for this call, and which storage it can write. The source file on a documentation site is a hint. The bytecode at the address, and any address it delegates to, is the program.
Deployment also has a receipt, and the receipt is not the code. A successful creation transaction gives you a contract address, a status, and the gas that was used. It does not give you a promise that the code does what the comments said. Failed creations do not leave runtime code at that address. A block explorer that shows a verified badge is showing a later, optional match between source and bytecode, performed by the explorer’s compiler, not by the protocol at the moment of deployment. The protocol’s record is the bytecode, the storage, and the address. Everything a human prefers to read has to be tied back to those three or it is commentary.
Sources
- Ethereum.org, Smart contracts.
- Ethereum.org, Compiling smart contracts.
- Ethereum.org, Ethereum virtual machine.
- Solidity documentation, introduction to smart contracts.
- EIP-7702, one mechanism that lets an externally owned account designate code.